Modernising a legacy system without stopping the business
Rewriting a critical system from scratch is one of the riskiest projects a business can take on. Incremental replacement is slower to describe and far safer to deliver.
Fintech & Financial Services
We design and build financial products and internal systems where correctness, security and a clear audit trail matter as much as the user experience.
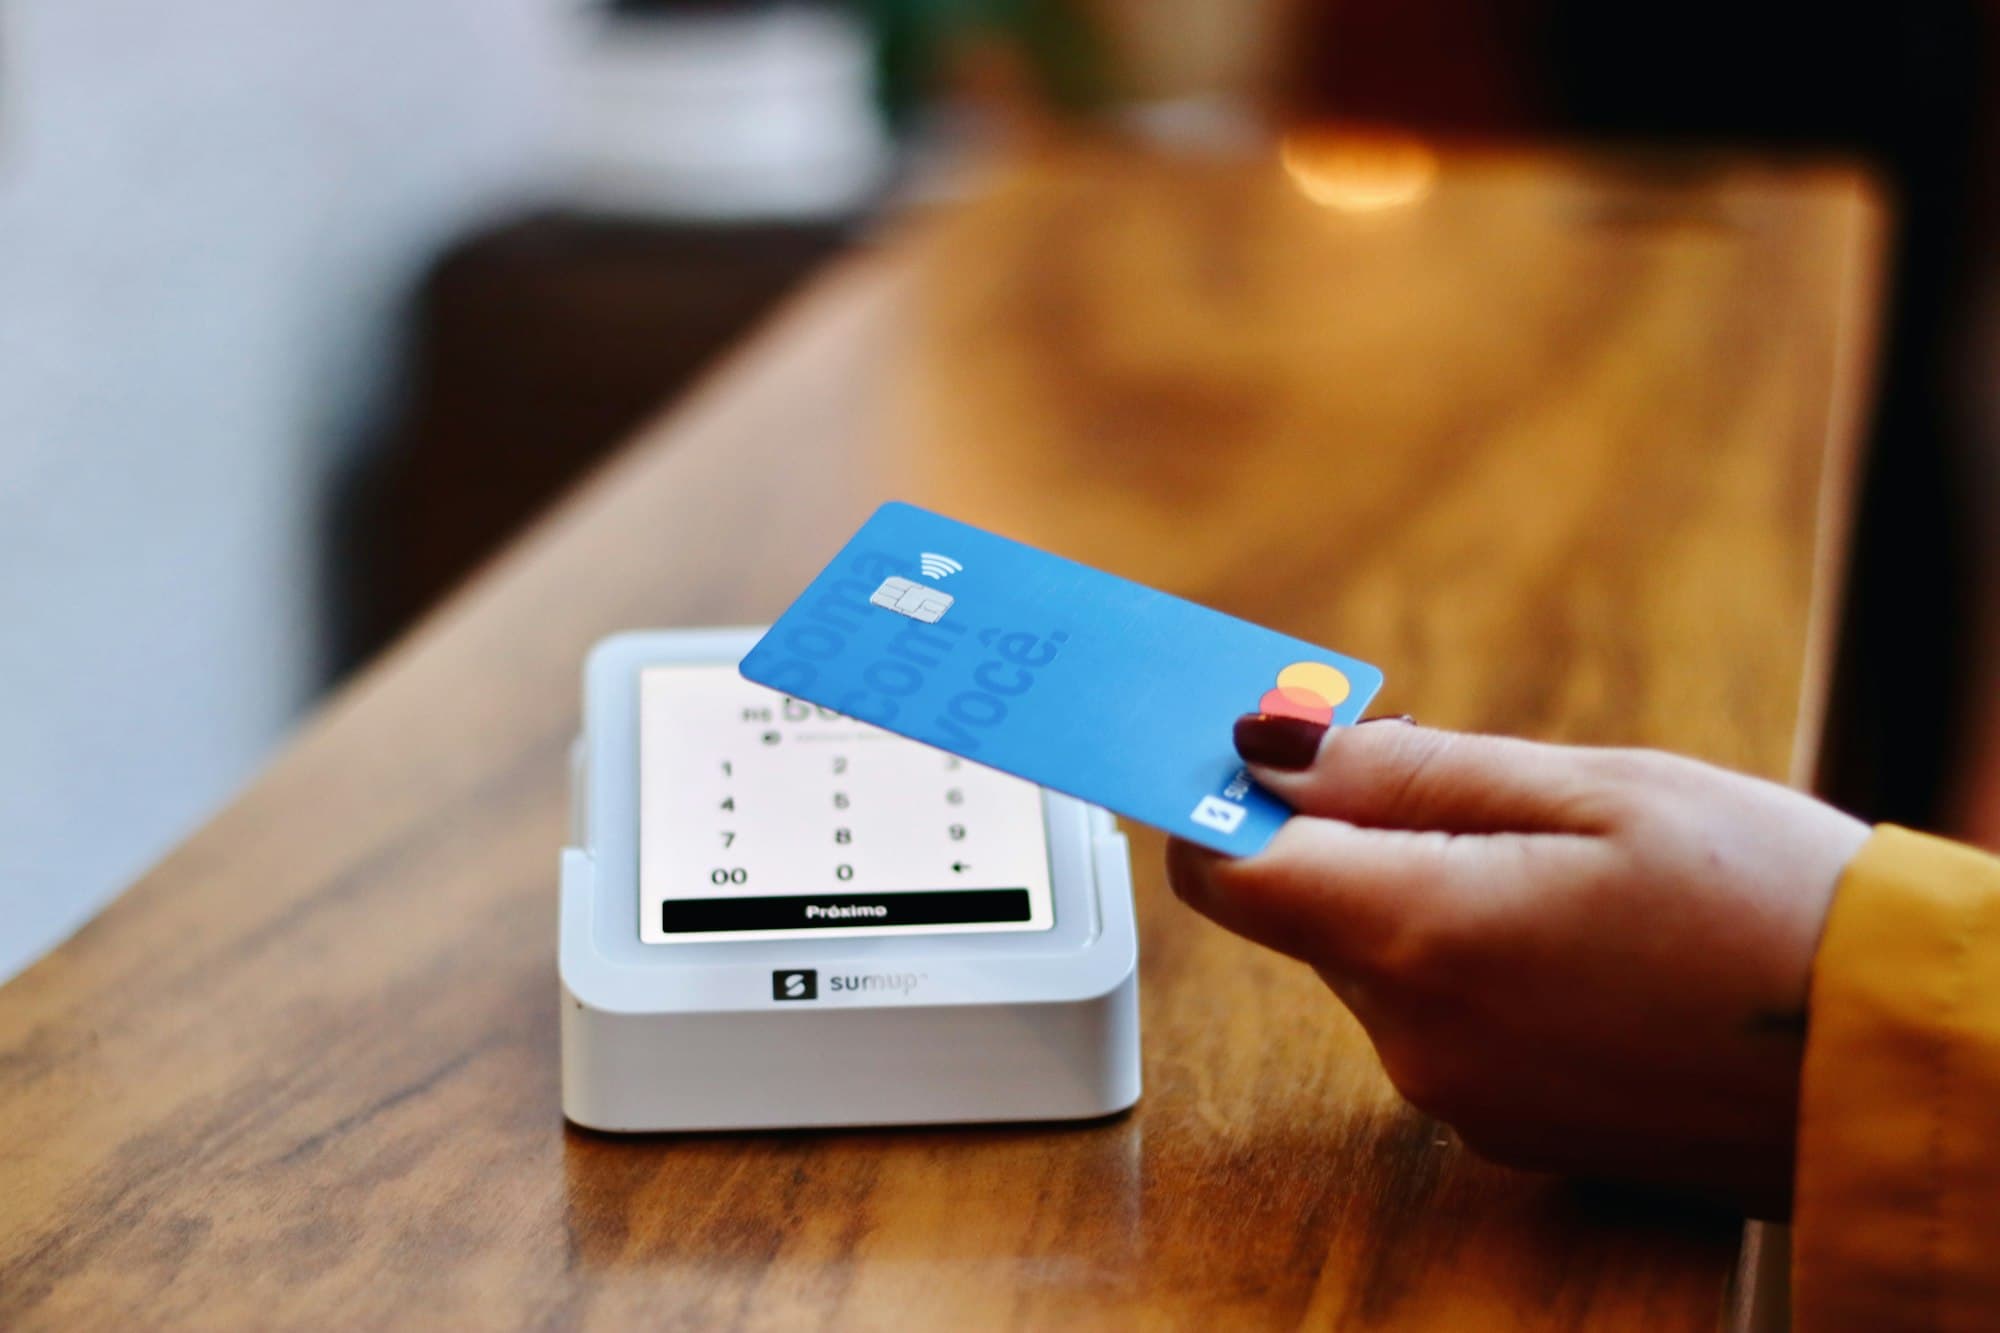
Financial services now run on software from end to end. Customers expect to open accounts, move money and see their position instantly, while firms rely on APIs for payments, identity checks, credit decisions and account data. Open Banking has made it normal to build products on top of other institutions' infrastructure, and embedded finance has put payments and lending inside non-financial products.
The engineering bar is different from most sectors. Money must never be created or lost by a bug, every material action needs to be explainable after the fact, and regulators expect firms to understand and control the systems and suppliers their services depend on. Good fintech software is often unremarkable on the surface and very careful underneath.
Balances calculated on the fly, floating-point arithmetic and missing idempotency lead to discrepancies that are expensive to investigate and hard to explain to auditors.
Know-your-customer and anti-money-laundering checks handled by email and spreadsheets slow onboarding and leave gaps in the evidence trail.
Ageing platforms and batch processes make it difficult to launch new products, expose APIs or provide the real-time experience customers expect.
Shared admin accounts and changes made directly in the database make it hard to show who did what, when and with what authority.
We model money as immutable ledger entries with precise decimal handling, and make every payment operation safe to retry, so balances always reconcile.
We integrate identity verification, sanctions screening and document checks into a single onboarding flow, with cases routed to your compliance team when a human decision is needed.
We wrap legacy systems with well-defined APIs and move functionality across in stages, so new products can launch without a risky big-bang migration.
We build role-based access, approval workflows and tamper-evident audit logs into the system from the start rather than adding them before an inspection.
Payment flows, wallets, payouts and subscription billing built on established providers, with reconciliation and dispute handling included.
Account information and payment initiation features built on Open Banking APIs, from affordability checks to pay-by-bank checkouts.
Application journeys, decisioning workflows, repayment schedules and servicing tools for lenders and brokers.
Case management for onboarding, transaction monitoring alerts and customer complaints, with a full record of decisions and evidence.
Where you are regulated, we work with your compliance team so the system supports your obligations on operational resilience, outsourcing oversight and fair treatment of customers, including clear documentation of how it works.
We build payment and account access flows that meet strong customer authentication requirements and handle consent, token expiry and bank API outages gracefully.
We keep raw card data out of your infrastructure by using tokenised payment providers such as Stripe, which substantially narrows the systems in scope for PCI DSS.
We design logging, retention and access so that transactions and decisions can be reconstructed for auditors, while still respecting UK GDPR data minimisation.
We work alongside regulated firms and their compliance teams, and design systems to support their obligations. We do not hold regulatory permissions ourselves and do not give regulatory advice; the firm's compliance function and advisers remain responsible for that, and we make sure the software gives them what they need.
We use a double-entry ledger with immutable entries, precise decimal types rather than floating-point numbers, idempotency keys on every payment operation and automated reconciliation against provider records. Discrepancies are flagged immediately rather than discovered at month end.
Yes. We typically work through an authorised aggregator rather than connecting to each bank directly, and design for the practical realities: consent renewal, inconsistent data between banks and occasional provider outages.
Usually, yes, by doing it in stages. We put an API layer in front of the existing system, move functionality across piece by piece and run old and new side by side where needed, so each step can be tested and reversed.
We build with secure defaults, automated dependency and code scanning, and least-privilege access in the cloud. For regulated products we recommend independent penetration testing before launch and after major changes, and we fix and document the findings.
Rewriting a critical system from scratch is one of the riskiest projects a business can take on. Incremental replacement is slower to describe and far safer to deliver.
Vague briefs produce quotes that cannot be compared. A few days of structured thinking before you contact suppliers will save weeks of confusion later.
Tell us what you are trying to achieve. The first conversation is about understanding the problem — not selling you a solution.